Do Small Businesses Need a Health and Safety Legal Register?

A clear look at legal obligations, business size, and why proportionate compliance matters.

It is a question we hear often from small business owners: โ€œDo I really need a health and safety legal register? Surely that’s something only for large companies with big compliance teams.โ€ It’s an understandable assumption, but it is not correct. Legal obligations in health and safety law are not switched on by company size โ€” they are triggered by what a business actually does, where it does it, and the risks that activity creates. A five-person joinery workshop and a five-hundred-person office may face entirely different legal duties, regardless of which one has more employees on the payroll.

In this article, we look at why the size of a business is the wrong starting point for thinking about legal compliance, and why a well-designed legal register โ€” far from being a burden reserved for large organisations โ€” can be one of the most practical and cost-effective tools a small business ever puts in place.

What Is a Health and Safety Legal Register?

A legal register is a structured record of the health and safety (and often environmental) legislation, regulations, and approved codes of practice that apply to a specific organisation. Rather than listing every law in existence, it identifies the ones that are actually relevant to that business’s operations, sites, and activities, and sets out what needs to be done to remain compliant with each one.

Done properly, a legal register becomes a single point of reference that tells a business owner or manager, at a glance: which laws apply to us, what each one requires, how we currently meet that requirement, and where any gaps exist.

Legal Obligations Depend on Circumstances, Not Company Size

This is the point worth dwelling on, because it is the one most often misunderstood. UK health and safety legislation is largely activity-based and risk-based rather than headcount-based. The Health and Safety at Work etc. Act 1974 and its supporting regulations apply to employers and the self-employed alike, and the specific duties that follow are shaped by factors such as:

  • The nature of the work being carried out (for example, construction, food handling, manual handling, or working with hazardous substances)
  • The premises involved and who else might be affected โ€” employees, contractors, visitors, or members of the public
  • Whether specific hazards are present, such as asbestos, fire risk, electrical systems, or work at height
  • Sector-specific rules that apply regardless of business size, such as food safety, licensing, or environmental permitting requirements

A single self-employed trades person using a ladder has duties under the Work at Height Regulations. A two-person catering business has duties under food hygiene and allergen legislation. A small manufacturer using solvents has duties under COSHH. None of these obligations disappear because the business is small โ€” in some cases, a smaller business with fewer resources to manage risk may need to pay closer attention, not less.

In other words, the question is never really โ€œis my business big enough for this to matter?โ€ The question is โ€œwhat do we actually do, and what does the law say about doing it safely?โ€ A legal register is simply the tool that answers that question clearly and keeps the answer up to date as legislation changes.

Why Small Businesses Benefit from a Concise, Proportionate Register

Recognising that legal duties apply regardless of size is only half the picture. The other half is that how a small business meets those duties can, and should, look very different from how a large organisation meets them. A 200-page legal register modelled on a multinational’s compliance framework is not only unnecessary for a small business โ€” it is actively counterproductive. It gets opened once, filed away, and forgotten.

Do small businesses need a health and safety legal register?

A legal register should be proportionate to your business activities

A register that is built specifically for a small business, scaled to its real activities and risks, tends to work far better in practice. This is why:

1. It Stays Usable

A concise register lists only the legislation that genuinely applies to that business’s operations. Instead of an overwhelming, generic checklist, the owner or manager is left with a short, relevant list they can actually refer to โ€” and act on โ€” day to day.

2. It Reflects the Business as It Really Operates

A bespoke register is built around the specific sites, equipment, substances, and work activities involved, rather than a one-size-fits-all industry template. This means it captures the obligations that matter and does not waste time on ones that do not.

3. It Makes Gaps Visible

Because it is proportionate rather than padded out, a well-built register makes it far easier to spot where compliance is solid and where attention is needed โ€” an outdated risk assessment, a missing policy, a licence due for renewal โ€” without those gaps being buried in irrelevant detail.

4. It Demonstrates Due Diligence

In the event of an incident, an inspection, or a client or insurer asking about compliance arrangements, a maintained legal register is tangible evidence that the business has identified its obligations and is actively managing them. For a small business without a dedicated compliance function, this matters a great deal.

5. It Supports Growth Without Starting from Scratch

As a small business takes on new work, new premises, or new equipment, a legal register built with the right structure can be updated and expanded rather than rebuilt. This means compliance grows alongside the business instead of becoming a sudden, overwhelming project further down the line.

Building a Register That Fits Your Business

The most effective legal registers for small businesses share a few common features: they are reviewed and updated regularly to reflect legislative change, they are written in plain language rather than legal jargon, they link each legal requirement to a clear action or evidence of compliance, and they are proportionate โ€” covering what applies, in appropriate detail, without unnecessary bulk.

This is where working with a health and safety consultancy adds real value. Rather than adapting a generic template, a consultancy can assess your specific activities and premises, identify the legislation that genuinely applies, and build a register that is both legally sound and genuinely usable by your team.

The Bottom Line

Health and safety law does not ask how many people are on your payroll before it applies to you โ€” it asks what risks your work creates. That means every business, regardless of size, has legal obligations worth identifying and managing properly. For small businesses, the smart response is not to ignore this reality, nor to adopt a compliance framework built for a much larger organisation. It’s to build a legal register that is concise, proportionate, and tailored to how the business actually operates โ€” one that gets used, kept current, and genuinely supports safer, more compliant day-to-day operations.

If you are unsure which legal requirements apply to your business, or you would like help building a legal register that is proportionate to your size and sector, our team can help you get a clear, practical picture of your obligations.

Would you like a free copy of our health and safety and environmental legal register checklist for UK operations?

What Happens if Your Legal Register is Out of Date?

A legislation registerโ€”or legal registerโ€”serves as the compliance anchor of an organisationโ€™s corporate governance structure and management system. Designed to identify, organise, and monitor all statutory duties and regulatory obligations applicable to an organisationโ€™s operations, it acts as the baseline for legal adherence. However, maintaining a legal register is not a one-time administrative task; it requires active upkeep to retain its utility.

The key risk of an outdated legal register is that it gives executive management a false picture of the organisationโ€™s true legal obligations and actual compliance level. While an outdated register may not immediately lead to criminal prosecution, relying on obsolete legal information creates subtle, compounding vulnerabilities across operational management, internal auditing, and ISO management systems.

Understanding the operational consequences of an outdated legal register highlights why static compliance documents fail to protect modern enterprises.


1. Missing Critical Legislative Changes and Statutory Amendments

Health, safety, and environmental statutory frameworks across Great Britain, Northern Ireland, the Isle of Man, and the Republic of Ireland are in constant motion. Regulators and parliaments amend existing legislation far more frequently than they enact entirely new primary Acts.

When a legal register is not updated regularly, the following issues occur:

  • Unrecorded Statutory Amendments: An entry in a register may list the correct title of an Act or Regulation, yet remain silently out of date because an amending statutory instrument altered a exposure threshold, broadened a legal definition, or moved a mandatory reporting deadline.
  • Retaining Revoked Legislation: Failing to remove repealed or revoked legislation creates unnecessary administrative clutter. This wastes valuable time during internal checks and misleads staff into enforcing duties that no longer exist under law.
  • Overlooking Updated Regulatory Guidance: Regulators such as the Health and Safety Executive (HSE) and the Environment Agency (EA) frequently update Approved Codes of Practice (ACOPs) and guidance documents. Although guidance is not always statutory law, it defines the legal benchmark expected by courts and enforcement inspectors. Missing these updates leaves operational procedures aligned with obsolete standards.

2. Flawed Compliance Assessments and Distorted Evaluations

Under international management standards such as ISO 14001 (Clause 9.1.2) and ISO 45001 (Clause 9.1.2), organisations must conduct periodic evaluations of their legal compliance status. A compliance evaluation tests operational reality against the parameters documented in the legal register.

If the underlying legal register contains out-of-date information, any subsequent compliance assessment becomes fundamentally flawed. Evaluating site practices against superseded statutory requirements generates inaccurate compliance scores. Managers receive reports indicating complete compliance, unaware that newly enacted statutory duties, altered discharge limits, or updated permit conditions have gone completely unassessed.


3. Failure to Identify New Obligations from Business Triggers

Legislative updates represent only one side of legal register maintenance; internal organisational changes represent the other. Updating a register solely on an annual schedule inevitably causes the document to lag behind internal operational developments.

A failure to execute trigger-based reviews means that routine commercial changes generate unmanaged legal exposure:

  • New Equipment and Machinery: Installing new plant or lifting machinery introduces obligations under the Provision and Use of Work Equipment Regulations 1998 (PUWER) or the Lifting Operations and Lifting Equipment Regulations 1998 (LOLER).
  • New Chemical Substances: Introducing new raw materials or cleaning agents can trigger the Control of Substances Hazardous to Health Regulations 2002 (COSHH) or REACH obligations.
  • Premises and Physical Footprint: Moving to new sites or altering existing buildings brings different fire safety orders, planning consents, and building regulations into scope.
  • Environmental Permit Variations: Varied abstraction consents, modified trade effluent limits, or altered waste classifications must be entered into the register the moment they are granted.
  • Cross-Border Expansion: Expanding operations into a new jurisdictionโ€”such as moving from Great Britain into Northern Ireland or the Republic of Irelandโ€”introduces an entirely separate body of legal requirements rather than a variation of existing rules.

Without a system that links operational changes directly to legal register reviews, new legal duties remain unidentified and unmanaged.


4. Incorrect Regulatory Risk and Misleading Executive Confidence

Executive leadership relies on corporate compliance reporting to evaluate organisational risk and allocate resources effectively.

An outdated legal register distorts this governance feedback loop. It provides leadership with a false sense of security, leading executives to believe that all statutory liabilities are isolated and controlled. In reality, unmonitored regulatory shifts accumulate quietly. This distorted view of regulatory risk can lead management to allocate compliance budgets in error, bypass necessary operational controls, or omit vital safety training.


5. Third-Party Audit Findings and ISO Non-Conformities

For organisations certified to ISO 9001, ISO 14001, or ISO 45001, the legal register is one of the most rigorously examined elements during third-party certification and surveillance audits.

Third-party auditors routinely evaluate legal registers using two distinct approaches:

  1. Top-Down Auditing: The auditor inspects a physical aspect or hazard on site (such as a chemical store, timber workshop, or waste area) and checks whether the corresponding statutory requirements and permit conditions are correctly detailed in the legal register.
  2. Bottom-Up Auditing: The auditor selects a specific entry within the legal register and requests live physical evidence demonstrating how that requirement is fulfilled on the ground.

If an auditor discovers that a register lacks recent legislative amendments, omits applicable permit conditions, or references revoked statutes, a formal non-conformity will be raised against Clause 6.1.3. Treating the legal register as a static, one-time exercise remains one of the most frequent causes of ISO audit failures.


6. Difficulty Demonstrating Legal Compliance and Due Diligence

Maintaining compliance requires more than listing statutory titles; it demands clear evidence of active oversight. A defensible legal register entries should link each statutory clause directly to an internal operating procedure, an assigned internal owner, and a verifiable evidence log.

If a regulatory inspector from the Health and Safety Executive (HSE) or Environment Agency (EA) inspects a site, or if an insurer evaluates an operational claim, an outdated register fails to demonstrate due diligence. Presenting a static document that has not been updated or audited within the preceding twelve months demonstrates a breakdown in compliance governance, making it difficult to prove that the business actively manages its statutory duties.


7. Breakdown of the Plan-Do-Check-Act Management Framework

Recognised management system frameworksโ€”such as ISO 45001 and HSG65โ€”operate on a continuous Plan-Do-Check-Act (PDCA) cycle.

Plan do check act. Legal register out of date?
Plan do check act cycle

The legal register forms the core foundation of the Plan stage. It defines what the organisation must comply with. If the Plan stage relies on obsolete statutory parameters:

  • Operational controls (Do) are built around incorrect standards.
  • Compliance audits (Check) evaluate performance against out-of-date criteria.
  • Corrective actions (Act) fail to address actual legal exposure.

When the legal register is disconnected from live operational checks, the entire management system fails to function as intended.


Establishing an Effective Legal Register Review Protocol

To prevent a legal register from becoming out of date, organisations should implement a dual-track review process:

  • Scheduled Legislative Reviews: Establish a fixed review schedule (typically quarterly) to monitor legislative changes, new statutory instruments, and updated regulator guidance across all operating jurisdictions.
  • Trigger-Based Internal Reviews: Integrate legal register review checklists directly into corporate change-management processes. Any change in business activities, premises, machinery, chemical usage, or environmental permits should prompt an immediate review.
  • Accountability and Audit Trails: Assign clear internal ownership for every entry and maintain a detailed audit trail showing when each requirement was last evaluated.

By pairing scheduled legislative monitoring with internal change management, executive leadership can ensure that the legal register remains an accurate, defensible reflection of the organisation’s legal duties.ย  To get help with your legal register, please contact one of our team.

How Often Should a Legal Register Be Updated?

How often should a legal register be updated? There is no single answer that fits every organisation, but there is a wrong answer: updating it once a year and hoping nothing important happened in between. A legal register is only useful if it reflects the law as it standsย today, and the law โ€” along with your business โ€” rarely stands still.

The honest answer is that a legal register needs two update cycles running side by side: a scheduled review (commonly quarterly) to catch legislative change, and a trigger-based review that fires whenever something changes inside your own organisation. Below is what should prompt each type of update, and why skipping either one leaves gaps.

Scheduled reviews: keeping pace with legislative change

Health and safety and environmental law changes constantly across every jurisdiction โ€” Great Britain, Northern Ireland, the Isle of Man and the Republic of Ireland all move independently, and a register built for one will not automatically cover another. A quarterly review is the practical minimum for most organisations; higher-risk sectors (chemicals, waste, construction, food) often benefit from monthly monitoring. Each cycle should specifically check for:

New legislation

Acts, regulations and statutory instruments do not announce themselves. New legislation should be added to the register as soon as it is in force (or, where lead time allows, flagged ahead of its commencement date so you are not scrambling to comply on day one).

Amendments to existing legislation

Legislation is amended far more often than it is replaced outright โ€” a threshold changed, a definition widened, a deadline moved. If your register only lists the original instrument, it is quietly out of date the moment an amending regulation takes effect, even though the entry still “looks” current.

Repealed and revoked legislation

Just as important as adding new law is removing what no longer applies. A register cluttered with revoked instruments does not just look untidy โ€” it wastes audit time and can mislead someone into thinking a duty still exists when it is been withdrawn.

New guidance

Approved Codes of Practice, Health and Safety Executive (HSE) and Environment Agency (EA) guidance, and equivalent guidance from Northern Ireland, the Isle of Man and Ireland’s regulators are not always legally binding, but they set the standard regulators and courts expect you to meet. Guidance updates should be tracked alongside the legislation they relate to.

Is your legal register regularly reviewed or just left on a shelf?

Trigger-based reviews: keeping pace with your own business

Legislative monitoring only tells half the story. The other half is recognising when something inside your organisation changes the law you are subject to. These triggers should prompt an immediate register review, not wait for the next scheduled cycle:

  • Changes in business activitiesย โ€” a new process, service line, or way of working can bring entirely new legal duties into scope.
  • New premisesย โ€” different buildings mean different building regulations, fire safety duties, planning conditions and local authority requirements.
  • New equipmentย โ€” new plant or machinery can trigger PUWER, LOLER, pressure systems, or work equipment regulations that weren’t previously relevant.
  • New chemicals or substancesย โ€” introducing a new substance can pull in COSHH, REACH, CLP, or storage and transport requirements, and may affect permit conditions.
  • Changes to environmental permitsย โ€” a varied permit, a new abstraction or discharge consent, or a change in waste classification all need reflecting in the register the moment they’re granted or amended.
  • Changes to applicable jurisdictionsย โ€” opening a site, taking on contracts, or employing staff in a new jurisdiction (say, expanding from Great Britain into Northern Ireland or the Republic of Ireland) means an entirely separate body of law applies, not a variation on the one you already have.

Building both cycles into one process

The most effective legal registers treat these two review types as complementary, not alternatives:

  1. Set a fixed scheduleย (quarterly is a sensible default) for legislative monitoring across every jurisdiction you operate in.
  2. Build a trigger checklistย into change-management processes โ€” procurement, facilities, HR and operations should all know to flag the business changes listed above.
  3. Assign ownershipย so it is clear whose job it is to action each type of update, not just who compiles the register.
  4. Keep an audit trailย of when the register was reviewed and what changed, which matters as much to auditors and regulators as the register’s content itself.

The bottom line

A legal register updated only once a year, on a fixed date, will always be behind โ€” both the law and the business move faster than that. Pair a quarterly (or more frequent) legislative review with a trigger-based process for internal change, and the register stays what it is meant to be: an accurate, defensible record of what applies to you right now.

Keeping a legal register current across multiple jurisdictions is exactly what our quarterly legislation updates are designed to support โ€” get in touch to find out how we can help.

What Does an ISO 14001 Legal Register Need to Contain?

If you are working towards ISO 14001 certification, or maintaining it, the legal register is one of the areas auditors return to again and again. As with its ISO 45001 counterpart, it looks straightforward on paper โ€” a list of environmental laws that apply to your business โ€” but in practice it is one of the most common sources of non-conformities.

This article follows on from our piece on the ISO 45001 legal register, and covers the environmental equivalent: what a compliant ISO 14001 legal register needs to contain, why it matters, and how to keep it audit-ready.

What Is a Legal Register Under ISO 14001?

A legal register for ISO 14001 (referred to in the standard as โ€œcompliance obligationsโ€) is a structured record of all the environmental laws, regulations, permits, consents, and other obligations that apply to your organisationโ€™s activities, products, and services.

Clause 6.1.3 of ISO 14001:2026 requires organisations to determine and have access to up-to-date compliance obligations related to its environmental aspects, to determine how these apply to the organisation, and to keep this information current. The register is how you evidence that this has been done.

It is worth noting that ISO 14001 deliberately moved away from the term โ€œlegal registerโ€ in favour of โ€œcompliance obligationsโ€ to reflect that the scope is broader than statute law โ€” but in practice, most organisations (and most auditors) still refer to it as the legal register, and we will use both terms here.

Why It Matters More Than It Looks

Just as with an OH&S legal register, this document is not a compliance checkbox โ€” it is the foundation your environmental management system (EMS) is built on. It drives your aspects and impacts assessment, your operational controls, your monitoring and measurement programme, and your internal audit criteria. If the register is wrong or incomplete, everything built on top of it is at risk too.

Auditors will typically test the register in two directions:

  • Top-down โ€” picking an environmental aspect (e.g. a waste stream, an emission point, a chemical store) and checking the relevant legislation is listed.
  • Bottom-up โ€” picking an entry in the register and asking how it is being met in practice, such as through a permit condition or monitoring record.

If either direction breaks down, it is usually flagged as a non-conformity.

Core Elements Every Entry Should Include

While the exact format can vary, a robust legal register entry should contain the following information for each requirement:

  1. Legislation or requirement title โ€” the specific act, regulation, permit, licence, or other obligation (e.g. environmental permit condition, corporate group standard, client contractual clause).
  2. Reference number or citation โ€” the official identifier so it can be traced back to source.
  3. Jurisdiction โ€” which country, state, or region it applies to, especially important for multi-site organisations with different permit regimes.
  4. Summary of the requirement โ€” a plain-language description of what the law or permit condition actually requires, avoiding a copy-paste of dense legal text. This is often where expert consultants can be beneficial in interpreting the requirement for your business operations.
  5. Applicability โ€” why and how this requirement applies to your specific sites, processes, or environmental aspects. Generic entries (โ€œEnvironmental Protection Act applies to all businessesโ€) are a common audit finding.
  6. Compliance status โ€” a clear statement of whether you currently comply, partially comply, or are working towards compliance. Particularly useful when first implementing ISO 14001.
  7. Evidence of compliance โ€” links or references to the specific permits, monitoring data, procedures, or records that demonstrate compliance.
  8. Responsible person or role โ€” who owns the register and is accountable for maintaining compliance.
  9. Review date and frequency โ€” when it was last checked and when it is next due for review.
  10. Source of update information โ€” how you monitor for changes (e.g. legislation update service, environmental regulator bulletin, trade body alert).
  11. Date of last legislative change โ€” useful for showing the register reflects the current version of the law or permit, not an outdated one.

Beyond Statutory Law: โ€œOther Requirementsโ€

Like ISO 45001, ISO 14001 explicitly extends beyond legislation to other compliance obligations the organisation has to, or chooses to, meet. These are easy to miss but often specifically probed by auditors. In an environmental context, they may include:

  • Environmental permits, licences, and consents (waste, water discharge, emissions to air)
  • Industry codes of practice and sector environmental guidance
  • Client or contractual environmental requirements
  • Corporate group environmental standards (for multi-site or multinational organisations)
  • Voluntary agreements, industry schemes, or accreditation body conditions
  • Producer responsibility obligations (e.g. packaging, WEEE, battery regulations)

If your register only lists statutory legislation and ignores these, it will not fully meet the clause requirement.

Your ISO 14001 legal register must include obligations as well as legislation

How to Structure the Register

There is no single structure every register must follow, and it is often shaped by the size, sector, and complexity of the organisation. Most organisations use a spreadsheet, a document, or a dedicated compliance software tool. Common groupings for an ISO 14001 register include:

  • General environmental legislation
  • Waste management and disposal
  • Water and effluent discharge
  • Air emissions
  • Hazardous and chemical substances
  • Energy and resource use
  • Sector-specific legislation (construction, manufacturing, healthcare, etc.)
  • Packaging and producer responsibility

Structuring it this way makes the register easier to cross-reference against your aspects and impacts register and operational controls, and much faster to navigate during an audit.

Keeping It Live: Review and Monitoring

A legal register is only useful if it stays current. ISO 14001 requires that this information be kept up to date, so your process needs to show:

  • A defined review frequency (many organisations review quarterly, with a full review annually)
  • A named responsible person for monitoring legislative and permit changes โ€” this can be an internal representative or an external consultant
  • A method for capturing changes (legal update subscription services are common, as manually tracking regulator publications is unreliable)
  • A record of how changes were assessed and, where relevant, action taken (updated aspects and impacts assessments, new controls, revised monitoring)

Common Mistakes to Avoid

  • Treating it as a one-off exercise. Registers built once for certification and never revisited are one of the most frequent non-conformities.
  • Copying generic templates without tailoring. A register that does not reflect your actual sites, processes, and environmental aspects will not withstand scrutiny.
  • No link to evidence. Listing a requirement without showing how it is actually met leaves a gap between the register and reality.
  • Missing permit conditions. Focusing only on primary legislation and overlooking the specific conditions attached to site permits and licences.
  • No ownership. Without a named responsible person, updates tend to fall through the cracks.

Do I Need a Legal Register for ISO 14001 Certification?

Yes. A legal register (compliance obligations register) is a mandatory requirement of Clause 6.1.3 and is one of the first documents an auditor will ask to see, both at initial certification and at every surveillance audit. Without one, an organisation cannot demonstrate it has identified and is managing its environmental compliance obligations, which is a core requirement of the standard.

Final Thoughts

A well-built legal register does more than satisfy Clause 6.1.3 โ€” it becomes a working tool that keeps your entire environmental management system grounded in what the law, your permits, and your other obligations actually require. Getting the structure right from the start, and building in a genuine review cycle, is what separates a register that passes audit from one that merely exists on paper.

If you are managing both standards together, it is worth reading this alongside our companion article on the ISO 45001 legal register โ€” many organisations choose to maintain a single combined register covering both health and safety and environmental obligations, provided it clearly distinguishes between the two.

If you would like support building or auditing your legal register as part of your ISO 14001 journey, get in touch with our team for a consultation.

What Does an ISO 45001 Legal Register Need to Contain?

If you are working towards ISO 45001 certification, or maintaining it, one of the most common sticking points during audits is the legal register. It sounds like a simple document โ€” a list of laws that apply to your business โ€” but auditors consistently find registers that are either incomplete, out of date, or too vague to demonstrate real compliance.

This article breaks down exactly what a compliant legal register needs to contain, why it matters, and how to keep it audit-ready.

What Is a Legal Register?

A legal register (sometimes called a “legal and other requirements register”) is a structured record of all the health and safety laws, regulations, codes of practice, and other obligations that apply to your organisation’s activities, products, and services.

Under ISO 45001, Clause 6.1.3 requires organisations to determine and have access to up-to-date legal requirements and other requirements relevant to their occupational health and safety management system (OH&S MS), and to keep this information current. The register is how you evidence that you have done this.

Legal register
Is your legal register up to date?

Why It Matters More Than It Looks

A legal register is not just a compliance checkbox. It is the foundation your OH&S management system is built on โ€” it drives your risk assessments, your operational controls, your training needs, and your internal audit criteria. If the register is wrong or incomplete, everything built on top of it is at risk too.

Auditors will typically test the register in two directions:

  • Top-down โ€” picking an activity or hazard on site and checking the relevant legislation is listed.
  • Bottom-up โ€” picking an entry in the register and asking how it is being met in practice.

If either direction breaks down, it is usually flagged as a non-conformity.

Core Elements Every Entry Should Include

While the exact format can vary, a robust legal register entry should contain the following information for each requirement:

  1. Legislation or requirement title โ€” the specific act, regulation, code of practice, standard, or other obligation (e.g. industry code, insurer requirement, client contractual clause).
  2. Reference number or citation โ€” the official identifier so it can be traced back to source.
  3. Jurisdiction โ€” which country, state, or region it applies to, especially important for multi-site organisations.
  4. Summary of the requirement โ€” a plain-language description of what the law actually requires, avoiding a copy-paste of dense legal text.ย  This is often where expert consultants can be beneficial in interpreting the law to your business operations.
  5. Applicability โ€” why and how this requirement applies to your specific operations, sites, or activities. Generic entries (“Health and Safety at Work Act applies to all businesses”) are a common audit finding.
  6. Compliance status โ€” a clear statement of whether you currently comply, partially comply, or are working towards compliance.ย  This is particularly useful when first implementing ISO 45001.
  7. Evidence of compliance โ€” links or references to the specific procedures, records, permits, certificates, or controls that demonstrate compliance.
  8. Responsible person or role โ€” who owns the register and is accountable for maintaining compliance.
  9. Review date and frequency โ€” when it was last checked and when it is next due for review.
  10. Source of update information โ€” how you monitor for changes (e.g. legislation update service, trade body bulletin, government gazette, etc.).
  11. Date of last legislative change โ€” useful for showing the register reflects the current version of the law, not an outdated one.

Beyond Statutory Law: “Other Requirements”

ISO 45001 explicitly extends beyond legislation to “other requirements.” These are easy to miss but often specifically probed by auditors. They may include:

  • Industry codes of practice and guidance documents
  • Client or contractual health and safety requirements
  • Relevant insurance provider conditions
  • Corporate group standards (for multi-site or multinational organisations)
  • Voluntary agreements or membership scheme conditions
  • Permits, licences, and consents tied to specific sites or activities

If your register only lists statutory legislation and ignores these, it will not fully meet the clause requirement.

How to Structure the Register

There is no single structure that every register must follow, and it is often determined by the type, size or nature of the organisation itself.  Most organisations use a spreadsheet, text document or a dedicated compliance software tool. Common groupings include:

  • General health and safety legislation
  • Fire safety
  • Environmental (where it overlaps with H&S, e.g. hazardous substances)
  • Sector-specific legislation (construction, manufacturing, healthcare, etc.)
  • Equipment and machinery
  • Chemical and hazardous substances
  • Transport and vehicles
  • Welfare and employment law touching on H&S

Structuring it makes the register easier to cross-reference against your risk assessments and operational controls, procedures and much faster to navigate during an audit.

Keeping It Live: Review and Monitoring

A legal register is only useful if it stays current. ISO 45001 requires that this information be kept up to date, so your process needs to show:

  • A defined review frequency (many organisations review quarterly, with a full review annually)
  • A named responsible person for monitoring legislative changes, this can be a representative in the organisation but could also be an external consultant
  • A method for capturing changes (legal update subscription services are common, as manually tracking government publications is unreliable)
  • A record of how changes were assessed and, where relevant, actioned (updated risk assessments, new controls, revised training)

Common Mistakes to Avoid

  • Treating it as a one-off exercise. Registers built once for certification and never revisited are one of the most frequent non-conformities.
  • Copying generic templates without tailoring. A register that does not reflect your actual sites, activities, and hazards will not withstand scrutiny.
  • No link to evidence. Listing a requirement without showing how it is actually met leaves a gap between the register and reality.
  • Missing “other requirements.” Focusing only on statute law and ignoring client, insurer, or industry obligations.
  • No ownership. Without a named responsible person, updates tend to fall through the cracks.

Final Thoughts

A well-built legal register does more than satisfy Clause 6.1.3 โ€” it becomes a working tool that keeps your entire OH&S management system grounded in what the law and your other obligations actually require. Getting the structure right from the start, and building in a genuine review cycle, is what separates a register that passes audit from one that merely exists on paper.

If you would like support building or auditing your legal register as part of your ISO 45001 journey, get in touch with our team for a consultation.

Health & Safety Legal Register vs Compliance Audit: What is the Difference?

If you have been told you need a “legal register” and separately advised to commission a “compliance audit,” you could be forgiven for wondering whether these are two names for the same thing. They are not โ€” and understanding the difference matters, because most organisations that fall foul of a health and safety enforcement notice have one of these two documents in place but not the other.

This article explains what each one actually does, how they work together, and which one your organisation needs first.

The short answer

A health and safety legal register identifies which legal requirements apply to your organisation. A compliance audit (or compliance evaluation) tells you whether you are actually meeting them.

One is a map. The other is a health check against that map. You need both, but they answer different questions, and confusing them is one of the most common gaps we find when we review a client’s health and safety management system.

Health and safety consultant reviewing legal register documentation

What is a legal register?

A legal register is a structured record of the health and safety legislation, regulations, approved codes of practice, and other legal requirements that apply to your organisation’s specific activities, sites, and operations.

A good legal register will typically:

  • List each applicable piece of legislation (for example, the Management of Health and Safety at Work Regulations, COSHH, the Work at Height Regulations, or sector-specific rules)
  • Summarise what that legislation requires of your organisation
  • Identify which parts of your business or which activities the requirement applies to
  • Identify the controls in place to meet the legal requirements
  • Be reviewed and updated as legislation changes or your operations evolve

Crucially, a legal register is a document of applicability. It answers the question: “What law applies to us, and what does it say we must do?” It does not, by itself, tell you whether you are doing it.

What is a compliance audit or evaluation?

A compliance audit takes the requirements identified in the legal register (or an equivalent framework) and tests them against reality. It asks: “Are we actually meeting this requirement, in practice, today?”

A compliance audit typically involves:

  • Site visits and observation of actual working practices
  • Review of documentation, records, and evidence (permits, training records, inspection logs, risk assessments)
  • Interviews with staff, supervisors, and duty holders
  • Gap analysis against each legal requirement
  • A findings report ranking non-conformities by risk and urgency
  • Recommendations and an action plan to close the gaps

Where the legal register is a snapshot of obligations, the compliance audit is a live assessment of performance. It is the difference between having a checklist and actually checking the boxes โ€” and finding out, in evidence-based detail, which ones you cannot honestly tick yet.

Legal Register

  • Records applicable legislation for the organisation

  • Sets the bench mark for compliance

  • Must be regularly reviewed & updated

  • Identifies controls in place

  • Bespoke to the organisation

  • Can be one jurisdiction or more

Compliance Audit

  • Identifies if you actually meet the legal requirements

  • Assesses at a specific point in time

  • Site visits, observations & staff interviews

  • Review of documentation, records, etc.

  • Gap analysis

  • Recommendations & action plan

Why the difference matters

We regularly see organisations that have invested in one of these tools and assumed it covers the other. Both mistakes carry real risk.

Legal register without an audit: You know what the law requires, but nobody has verified whether it’s happening on the ground. This is common where a legal register was purchased as a subscription product or generated once and filed away. It creates a false sense of security โ€” the document exists, so the box feels ticked, but there is no evidence of actual conformance if an inspector, insurer, or regulator asks for it.

Audit without a legal register: You get a snapshot of current practice, but without a clear, maintained baseline of what should apply, the audit scope is often built from generic checklists or the auditor’s working knowledge rather than your organisation’s specific legal exposure. Gaps in obligations you did not know applied to you can be missed entirely.

Used together, the legal register defines the scope of what to check, and the audit provides the evidence of whether you are meeting it. This combination is also what regulators, insurers, and courts expect to see when assessing whether an organisation exercised due diligence โ€” a legal register with no corroborating evidence of compliance checking is a weak defence in an enforcement case or civil claim.

How they fit into a health and safety management system

Think of it as a three-stage cycle:

  1. Identify โ€” the legal register captures every applicable requirement
  2. Evaluate โ€” the compliance audit tests current practice against each requirement
  3. Act โ€” a corrective action plan closes the gaps the audit identifies, and the cycle repeats on a review schedule

This mirrors the “Plan-Do-Check-Act” approach that underpins recognised health and safety management standards such as ISO 45001 and HSG65. A legal register alone only covers “Plan.” Without the “Check” stage โ€” the audit โ€” you have no mechanism to confirm the plan is working.

Which do you need first?

If your organisation does not currently have a legal register, that is the logical starting point โ€” you cannot meaningfully audit compliance against requirements you have not formally identified.

If you already have a legal register but it has not been tested against actual site practice in the last 12 months, a compliance audit should be your next step. An out-of-date or unverified register can quietly become a liability rather than an asset.

Get a clear picture of your legal exposure and compliance status

Many organisations discover during an audit that gaps have existed for months or years without anyone noticing โ€” often because the legal register and the audit process were never properly connected.

If you are not sure whether your current legal register is complete, whether your last audit was thorough enough, or where to start with either, we can help. We carry out legal register development, gap analysis, and full compliance audits tailored to your sector and operations, with a clear, prioritised action plan at the end of it โ€” not just a list of problems. We have experience in a variety of sectors to meet your needs.

Get in touch to arrange a no-obligation discussion about your current legal register or compliance status, and we will tell you honestly where your priorities should be.

How to Pinpoint Environmental Legislation for Your Business

Environmental compliance can feel like an impossible maze. Regulations pile up at the local, national, and sometimes international level. They also shift depending on your industry, your size, your location, and even the specific materials you handle. Many business owners freeze at this point, assuming they need a law degree just to figure out where to start.

The good news is that you do not. You do not need to become an environmental lawyer, but you do need to know which requirements apply to your operations. This article walks through a practical process for narrowing down the environmental legislation for businesses that actually matters to your business, so you can focus your time and resources on real compliance instead of guesswork.

Why This Matters Before You Even Start

Non-compliance with environmental law is not a minor administrative slip. Depending on jurisdiction, penalties can include significant fines, operational shutdowns, personal liability for directors, and reputational damage that outlasts any fine. On the other hand, over-compliance โ€” spending resources chasing rules that do not apply to you โ€” wastes money and attention that could go toward growth. Getting the scope right is the foundation of an efficient compliance program.

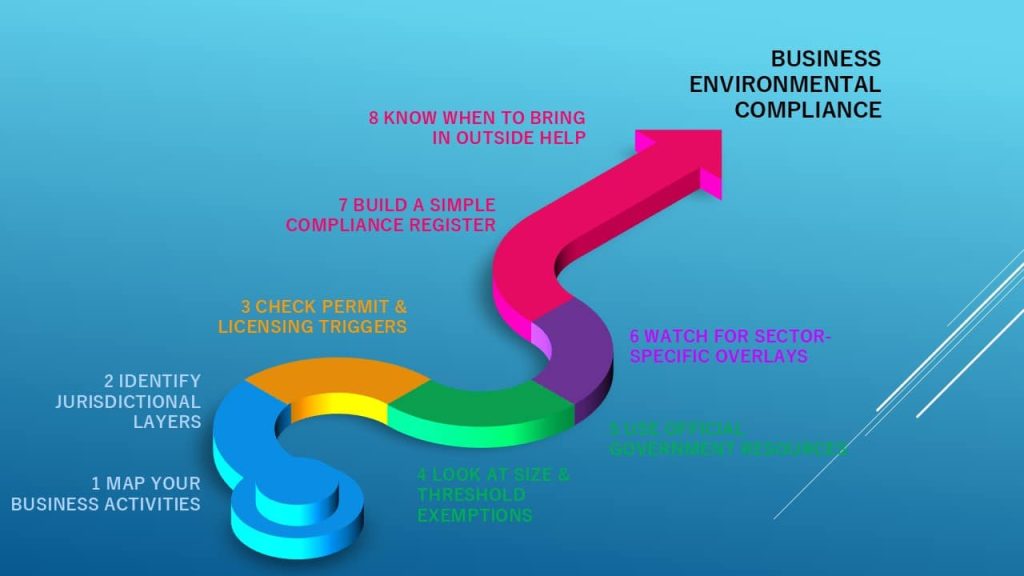
Step 1: Map Your Business Activities, Not Just Your Industry

Legislation is often triggered by specific activities rather than by industry labels. A “manufacturing” business might trigger air emissions rules because of a paint booth, water discharge rules because of a wash-down process, and hazardous waste rules because of solvent disposal โ€” three separate regulatory regimes from three separate activities.

Start by listing:

  • What raw materials, chemicals, or substances you use, store, or produce
  • What waste streams your operations generate (solid, liquid, air, hazardous)
  • Whether you discharge anything to water, air, or land
  • Whether you import, export, transport, or store regulated goods
  • The physical footprint of your operations (land use, proximity to protected areas or waterways)

This activity-based map is usually far more useful than starting from your business’s official industry classification.

Environmental compliance journey

Step 2: Identify Your Jurisdictional Layers

Environmental law is rarely a single rule book. Most businesses need to check multiple layers:

  • Local rules โ€” SSSI designations, noise, local waste collection and disposal by-laws
  • National legislation โ€” overarching frameworks such as clean air, clean water, or waste management Acts or Statutory Instruments
  • International or trade-related obligations โ€” relevant if you import/export goods or waste, use certain packaging, or operate across borders

A rule of thumb: start at the national level to understand the broad framework, then narrow down to local rules, which often add stricter or more specific obligations on top.

Step 3: Check for Permits and Licensing Triggers

Many environmental obligations are tied to permits rather than blanket rules. Common triggers include:

  • Emitting pollutants above a certain threshold
  • Discharging wastewater
  • Storing hazardous substances above specified quantities
  • Operating certain types of equipment (boilers, generators, refrigeration systems with regulated refrigerants)
  • Extracting or using groundwater

If any of these apply, there is likely a permitting authority you need to register with, and permits often come bundled with monitoring, record keeping, and reporting duties.

Step 4: Look at Size and Threshold Exemptions

Many environmental regulations include size-based thresholds โ€” for example, exemptions or reduced obligations for small quantity generators of waste, or simplified reporting for smaller emitters. Do not assume a regulation applies in full just because it mentions your industry; check the thresholds carefully, since they can significantly change your compliance burden.

Step 5: Use Official Government Resources

Regulatory agencies typically publish guidance documents, compliance checklists, and industry-specific fact sheets designed for non-specialists. These are usually more current and more directly applicable than general online summaries. Useful sources include:

  • National environmental protection agency websites such as the Environment Agency in England and Wales, SEPA in Scotland
  • State or provincial environment department portals such as DEFRA and DAERA
  • Local council or municipal planning and environmental health offices
  • Industry association compliance guides

Step 6: Watch for Sector-Specific Overlays

Certain sectors carry additional layers of regulation on top of general environmental law โ€” food and beverage, construction, agriculture, manufacturing, healthcare, and mining are common examples. If you operate in one of these sectors, check for sector-specific statutes or codes of practice in addition to general environmental legislation.

Step 7: Build a Simple Compliance Register

Once you have identified applicable legislation, do not leave it in your head or in scattered notes. Build a basic register or registers that track:

  • The specific regulation or permit requirement
  • The regulating authority
  • Renewal or reporting deadlines
  • The internal person responsible / procedure applicable
  • Evidence or records required to demonstrate compliance

This turns a one-time research exercise into an ongoing management tool.

Step 8: Know When to Bring in Outside Help

Self-assessment gets you most of the way, but some situations warrant professional input โ€” complex permitting processes, contaminated land issues, mergers or acquisitions involving environmental liabilities, or any situation where the penalties for getting it wrong are severe.

Environmental consultants and lawyers are most valuable when used strategically and will provide real value to the process.

The Benefits of Bringing in an External Consultant

Even with a solid self-assessment process in place, an external environmental consultant can add real value. Consultants work across many businesses and jurisdictions, so they tend to spot applicable legislation and emerging regulatory changes faster than an internal team researching the topic for the first time.

Consultants can also benchmark your operations against industry-specific obligations you might not think to check, verify that thresholds and exemptions have been applied correctly, and flag overlapping requirements between local and national regulators before they become a problem.

Beyond the initial identification exercise, a consultant can help translate legislation into practical action โ€” building or auditing your compliance register, preparing permit applications, and liaising directly with regulators on technical points. For businesses expanding into new activities, new sites, or new jurisdictions, this outside expertise often pays for itself by preventing costly missteps, reducing the time your team spends on unfamiliar regulatory research, and giving management confidence that nothing material has been missed.

Final Thoughts

Identifying which environmental legislation applies to your business is less about legal expertise and more about a structured process. Understand your activities, map the jurisdictional layers, check permitting triggers and thresholds, use official guidance, and keep a living record of what applies. Approached this way, environmental compliance becomes a manageable, ongoing part of running your business rather than an intimidating unknown.

If you would like to see how we can help you identify which environmental legislation applies to your business, please contact one of our team.

Why not download our health and safety and environmental legal register checklist for UK operations.

How to Identify Which Health & Safety Legislation Applies to Your Business

UK health and safety law is not a single rule book that every business follows in the same way. Instead, it’s a layered system: the Health and Safety at Work etc. Act 1974 (HSWA) sets out broad duties that apply to almost every employer, while dozens of more specific regulations โ€” made under that Act โ€” only apply depending on what your business actually does. Many owners and managers assume that because they have done a general risk assessment, they are covered. In practice, working out your full legal obligations means looking closely at your activities, equipment, premises and workforce, not just your industry label.

This article walks through the main factors that determine which UK regulations apply to your business, so you can build an accurate picture of your legal duties rather than relying on guesswork.

Start with the general duties under HSWA 1974

The Health and Safety at Work etc. Act 1974 is the foundation of UK health and safety law. It places a general duty on employers to ensure, so far as is reasonably practicable, the health, safety and welfare of their employees, and to protect others โ€” such as contractors, visitors and the public โ€” who may be affected by their work. The Act also places duties on the self-employed and on those in control of premises.

HSWA rarely tells you exactly what to do in a given situation. Instead, it is supported by a wide range of secondary legislation โ€” mostly Statutory Instruments enforced by the Health and Safety Executive (HSE) or your local authority โ€” that add specific, practical requirements. Identifying which of these regulations apply to you depends on several interacting factors.

Houses of Parliament, London

Factor 1: The nature of your work activities

The single biggest driver of applicability is what your business actually does day to day. UK regulations are often built around specific hazards or types of work, meaning two businesses in the same broad sector can have quite different legal obligations depending on the tasks involved. Common examples include:

Each of these activities brings its own dedicated regulations into scope, separate from the general HSWA duties.

Factor 2: The substances and materials you work with

If your business handles chemicals, dust, fumes, biological agents or other hazardous substances, the Control of Substances Hazardous to Health Regulations 2002 (COSHH) is likely to apply โ€” regardless of your sector. This is not limited to obviously “industrial” settings; hairdressers, cleaners, print shops, laboratories and even offices using certain equipment can fall within scope. Applicability depends on the substance itself, how it is used and stored, and the level of exposure risk โ€” not on your business type. Where lead or asbestos are involved specifically, separate dedicated regulations apply on top of COSHH.

Factor 3: Equipment and machinery in use

The Provision and Use of Work Equipment Regulations 1998 (PUWER) generally applies wherever machinery, tools or equipment are used for work โ€” from industrial plant to a simple stepladder or a piece of office equipment. Where lifting equipment is involved (hoists, forklifts, lifts), the Lifting Operations and Lifting Equipment Regulations 1998 (LOLER) also applies, and pressure systems bring in the Pressure Systems Safety Regulations 2000. The trigger here is the presence and use of the equipment itself, not the sector you operate in.

Factor 4: Your premises and how they are used

The type of premises you occupy, and how they are used, brings separate legislation into play:

A business operating from a warehouse, a shop, a construction site or a shared office block may each face different obligations relating to the physical environment, even where their core work activity is otherwise similar.

Factor 5: The size and structure of your business

Some duties scale with headcount. Under the Management of Health and Safety at Work Regulations 1999, employers with five or more employees must record significant findings of their risk assessments in writing and have a written health and safety policy. Businesses below that threshold still carry the same underlying legal duty to manage risk โ€” they simply have lighter documentary requirements. Separately, if you employ anyone, you are generally required to hold Employers’ Liability Insurance under the Employers’ Liability (Compulsory Insurance) Act 1969, with limited exemptions.

Factor 6: Who is affected by your work

UK legislation does not only protect your direct employees. HSWA and related regulations also require you to consider contractors, visitors, and members of the public affected by your activities. This is particularly relevant if you:

  • Invite the public onto your premises (retail, hospitality, leisure)
  • Send staff to work on other organisations’ sites
  • Manage shared workspaces where multiple employers’ activities interact

The Reporting of Injuries, Diseases and Dangerous Occurrences Regulations 2013 (RIDDOR) also applies broadly here โ€” requiring certain injuries, diseases and dangerous occurrences to be reported to the HSE, regardless of whether the person affected was an employee.

Factor 7: Your sector-specific regulatory regime

Certain industries carry their own dedicated regulatory frameworks layered on top of general health and safety law, including:

  • Construction โ€” CDM Regulations 2015
  • Agriculture โ€” regulations covering machinery guarding, livestock handling and pesticides
  • Food businesses โ€” food hygiene regulations sit alongside (not instead of) health and safety law
  • Healthcare โ€” additional infection control and clinical waste regulations
  • Transport and logistics โ€” drivers’ hours rules and vehicle-specific regulations

These sector-specific rules typically sit alongside general legislation like HSWA and the Management Regulations, rather than replacing them.

Factor 8: Enforcement authority and regional variation

In Great Britain, enforcement is split between the HSE (typically for higher-risk sectors like construction, manufacturing and agriculture) and local authorities (typically for offices, retail and hospitality) โ€” it is worth knowing which applies to your business, as this affects who you report incidents to and who may inspect your premises. Note also that Northern Ireland has its own health and safety legislative framework, enforced by the Health and Safety Executive for Northern Ireland (HSENI), which mirrors but is legally separate from GB law. Businesses operating across the UK should check they are not assuming GB regulations automatically extend to Northern Ireland.

Putting it together: a practical approach

Rather than trying to memorise every regulation that might apply, it is more effective to map your business against these factors systematically:

  1. List your work activities โ€” every task carried out by staff, not just the “main” job.
  2. List the substances, equipment and materials involved in each activity.
  3. Map your premises types and how each is used, including shared or third-party sites.
  4. Check your headcount against the five-employee threshold for written documentation.
  5. Identify who else is affected โ€” contractors, visitors, the public.
  6. Check for sector-specific regimes relevant to your industry.
  7. Confirm your enforcing authority (HSE or local authority) and whether Northern Ireland rules apply.

Working through this list will usually surface a shortlist of applicable regulations that goes well beyond HSWA’s general duties alone. Because legislation is periodically updated, it is worth revisiting this exercise whenever your activities, premises or workforce change significantly โ€” and consulting a qualified health and safety adviser or solicitor if you are uncertain how a specific regulation applies to your circumstances.

Getting this right is not just about compliance for its own sake. Understanding exactly which legislation applies to your business is the foundation for building risk assessments, policies and training that address the hazards your people actually face โ€” rather than a generic checklist that misses what matters most.

Determining which legislation is applicable in your business can be complicated and time consuming, although the Health and Safety Executive acknowledges that businesses need to identify the laws relevant to their particular industry and activities.

We identify the health & safety legislation relevant to your specific activities and produce a bespoke legislation register.  We can also provide a regular update service so that you can focus on running your business.  If you would like a quotation or more information about the services we offer, please contact us.

Would you like a free copy of our health and safety and environmental legal register checklist?

Click here

Proven: Skip Boss Receives a Suspended Prison Term

A skip boss of a business near Braintree that hires out rubbish skips has been sentenced to a 6-month suspended prison term.

Chelmsford magistratesโ€™ court heard about Roy Brettโ€™s โ€œrepeated failureโ€ to accept Environment Agency warnings regarding overflowing skips and uncovered waste. Brettโ€™s company, RJ Brett Contracts Ltd, was fined ยฃ3,000 for similar offences.

Chair of the bench Andrew McGregor said the site โ€œposed multiple risks to the environment and human safety, including by fire.โ€

yard full of waste
The yard was full of wood, metal, textiles and buildersโ€™ rubbish.ย 

Between 2024 and this year, Brett refused to comply with repeated orders.

However, Skip boss Brettโ€™s inaction allowed the waste to overflow from an ever-growing number of skips.

Additionally, the site was exposed to the elements, with no sealed drainage.

Roy Brettโ€™s yard is nestled in green fields near Braintree, but he ignored repeated warnings about the number of skips and amount of waste built up at the site

The yard was full of wood, metal, textiles and buildersโ€™ rubbish. Hardly any space was left, causing a fire-risk, and a lot of waste was just stored on the ground.  

Brett had claimed he โ€œdidnโ€™t do e-mails,โ€ so โ€œmissedโ€ written instructions to remove the waste, piled up across the site. But the Environment Agency also warned him in person.

He didnโ€™t have an environmental permit to manage the yard, but finally, after lots of excuses and denial when challenged by the Environment Agency, Brett admitted in court to breaching environmental law. RJ Brett Contracts Ltd was also charged.

Brett faces a custodial sentence if he commits other offences or doesnโ€™t clear the site by November.

Lesley Robertson, enforcement team leader for the Environment Agency in Essex, Norfolk and Suffolk, said:

โ€œIt wasnโ€™t credible for an operator like Roy Brett, director of three other waste companies and years of experience, to say he misunderstood the need for an environmental permit or justify having an exemption from needing one. 

โ€œThe operation undercut rivals by avoiding permitting and subsistence fees. They also evaded permit conditions designed to protect the environment.โ€

Essex County Fire and Rescue Service had concerns about the site, too. They told Brett to tidy up the yard, and make sure no waste that could start a fire was brought in.       

The Environment Agency began an investigation into the site in July 2024. Officers found more than a dozen skips brimming with waste. Brett was given 3 months to remove it all.    

Officers were back on site when the deadline passed as the situation hadnโ€™t improved. Brett was then warned the site must be cleaned up, or face prosecution. By early 2025, almost 50 skips filled the yard, some on top of others. Officers also saw large piles of wood and soil. There were also problems with smells.

Brett sought to legitimise his waste operation by registering exemptions from environmental permits that are meant for low-risk activity. But the Environment Agency deregistered the exemptions when the site took on too much waste.   

As well as the order to remove all waste, the 66-year-old, of Winstree Road, Stanway, in Colchester, was sentenced to 6 months in prison, suspended for 18 months. He was ordered to undergo 30 days of rehabilitation activities and told to pay a ยฃ154 victim surcharge.

RJ Brett Contracts Ltd was fined ยฃ3,000 and must pay a victim surcharge of ยฃ1,200, in relation to breaches of the waste removal order. The penalties accompany the custodial sentence and relate to the companyโ€™s involvement in those offences.

RJ Brett Contracts Ltd was charged with 4 offences:

  • operating the waste facility at Lanham Green Road in Cressing, without an environmental permit between 3 July 2024 and 31 January 2025;
  • and between 1 February 2025 and 30 January 2026, both contrary to regulations 12 and 38 (1)(a) of the Environmental Permitting (England and Wales) Regulations 2016;
  • failing to comply with a notice dated 28 November 2024, requiring the company to remove controlled waste from the site by 30 January 2025, contrary to sections 59ZB(2) and 59ZB(6) of the Environmental Protection Act 1990;
  • and keeping controlled waste at the site in a manner likely to cause environmental pollution or harm to human health, contrary to section 33(1)(c) contrary to Section 33(1)(c) of the Environmental Protection Act 1990.

Roy Brett was also charged with 4 offences:

  • contrary to regulations 12, 38(1)(a) and 41(1) of the Environmental Permitting (England and Wales) Regulations 2016, knowing of or contributing to operation of the waste facility at Lanham Green Road, in Cressing, by RJ Brett Contracts Ltd, without an environmental permit between 3 July 2024 31 January 2025;
  • and between 1 February 2025 and 30 January 2026;
  • contrary to section 59(5) and s157(1) of the Environmental Protection Act 1990. knowing of or contributing to RJ Brett Contracts Ltd failing to comply with a notice dated 28 November 2024 served on the company, requiring it to remove controlled waste from the site by 30 January 2025;
  • contrary to sections 33(1)(c) and 157 of the environmental Protection Act 1990, knowing of or contributing to RJ Brett Contracts Ltd keeping controlled waste in a manner likely to cause pollution to the environment or harm to human health.

Anyone can check to see if a site is licensed to receive waste.ย  The register can be found on the Environment Agencyโ€™s website here.

If you require expert assistance for your waste business, please reach out to the Ashbrooke advisory team today.

The Essential Guide to Environmental Permit Management Systems

Executive Summary

An environmental permit management system provides a structured framework of procedures to minimise pollution risks from permitted activities.

For regulated waste management, mining, or installation facilities, maintaining a written management system is a regulatory requirement.

This document outlines statutory compliance frameworks, risk assessments, site planning, and operational records to satisfy Environment Agency expectations.

Regulatory context and application requirements

1. Regulatory Context and Application Requirements – Environmental permit management system

The scope and submission requirements depend on the nature of the application.

Moreover, the complexity of site operations determines the system needs, including โ€ข Environmental permit management system.

Additionally, Standard Rules permits the – Environmental permit management system.

  • Risk Identification: Specific operational risks are pre-determined within generic risk assessments.
  • Submission Protocol: You do not need to submit the system documentation during the application phase.
  • Deployment Deadline: The complete management system must be fully operational prior to commencing site activities.
  • Regulatory Assessment: Documentation is typically evaluated during the pre-operation site inspection by an Environment Agency officer.
  • Combustible Waste Provision: Standard rules applications involving combustible waste storage require the concurrent submission of a robust Fire Prevention Plan (FPP).
Man sampling water

We manage bespoke permits through the environmental permit management system.

  • Risk Identification: Operational hazards must be explicitly identified via a site-specific risk assessment.
  • Submission Protocol: A comprehensive summary of the management system must be included as part of the formal application pack.
  • Water & Groundwater Exemptions: Standalone water discharge or groundwater activity applications (Forms B6.5 or B6.6) do not require advance submission of the management system summary, but the system must be fully implemented prior to operation.

2. Certified Environmental Management System (EMS) Standards. Additionally, they align with the environmental permit management system to meet regulatory requirements.

For large-scale or high-risk facilities, such as industrial installations and hazardous waste processing operations, the Environment Agency favours these systems.

Moreover, they are part of the environmental permit management system and are built around recognised international frameworks.

Utilising an independently verified system enhances regulatory confidence and can reduce inspections under the OPRA methodology.

As part of the environmental permit management system, operators must state if their system is modelled on accredited standards. Additionally, they should indicate whether it is modelled on any listed standards.

Note: Accredited certification (verified by UKAS) demonstrates robust governance, but it does not absolve the operator of liability.

However, this does not absolve the operator of liability for individual permit breaches within the environmental permit management system.

3. Site Infrastructure and Spatial Planning Requirements are addressed within the environmental permit management system.

Operators must compile scaled, detailed site plans showing where permits and exemptions take place within the environmental permit management system. Additionally, high-risk or complex sites frequently require multiple standalone drawings to fulfil regulatory requirements.

Core infrastructure components (Waste, Installations, and Mining) are central to the environmental permit management system.

Site plans for the management system must clearly mark the locations of the following assets.

Additionally, this relates to the environmental permit management system.

  • Structural Assets: Buildings, treatment facilities, incinerators, silos, and perimeter security fencing.
  • Hazardous Storage: Containment areas for oils, fuel tanks, chemical bunds, and raw waste stock.
  • Emergency Equipment: Spill kits, absorbents, and critical emergency response machinery.
  • Logistics Access: Dedicated entry and exit pathways for emergency service vehicles.
  • Pollution Control Points: Environmental monitoring stations, sampling points, and inspection manholes.
  • Effluent Infrastructure: Trade effluent or sewage treatment plants and final discharge outfalls.
  • Historical Liabilities: Any parcels of land with known or suspected historical ground contamination.

Additionally, mapping of drainage and utilities supports the environmental permit management system for regulatory compliance.

Drainage networks require precise colour-coding and directional labelling. Additionally, implementing an environmental permit management system supports consistent labelling and compliance.

  • Foul and Combined Drainage: Must be marked clearly in red.
  • Surface Water Drainage: Must be marked clearly in blue.
  • Flow Mechanics: Plans must display water flow direction, discharge connection points (to sewer, soak-away, or watercourse), manhole covers, interceptor tanks, and isolating stop/diverter valves.
  • Utility Routing: Main inlets and distribution paths for mains water, gas, and electricity must be charted, with explicit positioning of water stop taps and utility isolation switches.

Additionally, standalone water discharge and groundwater activities are managed under the environmental permit management system.

Furthermore, for point-source water and groundwater authorisations, the site plan must isolate within the environmental permit management system.

  • The wastewater treatment infrastructure.
  • Statutory sample collection and monitoring points.
  • Mitigation infrastructure and environmental emergency equipment.
  • The defined surface water outlet or groundwater infiltration system.
  • The designated field boundaries for land-spreading activities (where applicable).

4. Operational Control Plans and Specific Sub-Systems for the environmental permit management system.

A compliant management system breaks down site operations into distinct phases.

Additionally, start-up, normal operation, and shut-down are the phases for the environmental permit management system.

Operators must identify the environmental risks associated with each sub-process and outline specific mitigation actions.

Waste storage plans are integral to the environmental permit management system and ensure safe, compliant operations.

Waste facility operators must document an explicit waste storage strategy detailing.

In addition, this record should be maintained in the environmental permit management system.

  • Maximum storage duration thresholds for every distinct waste streams.
  • Control measures to prevent emissions during extended storage.
  • Absolute volume limits and maximum pile heights for all stored materials.
  • Waste identification procedures and strict segregation protocols for incompatible materials.
  • Pre-acceptance and acceptance procedures to prevent the receipt of unpermitted waste.

The environmental permit management system manages Fire Prevention Plans (FPP).

Facilities storing combustible waste must submit a standalone, robust Fire Prevention Plan detailing prevention, detection, containment, and mitigation measures.

Within the environmental permit management system, the Environment Agency assesses these plans stringently against hourly review rates.

Consequently, failing to secure approval on initial submission significantly elevates regulatory costs.

Site Condition Reports (SCR) relate to the environmental permit management system.

For installations, waste operations, and mining permits, a Site Condition Report must be maintained throughout the lifecycle of the permit. This document logs historical spills, baseline land/groundwater data, and evidence verifying effectiveness in the environmental permit management system. It serves as the primary legal benchmark when applying to surrender a permit.

Standalone Environmental Management Documents cover the environmental permit management system and its related compliance.

Depending on site risks, the Environment Agency will require separate, standalone document submissions for individual environmental vectors.

Consequently, this enables the environmental permit management system to support distinct internal specialist reviews.

  • Odour Management Plan (OMP)
  • Emissions Management Plan (EMP)
  • Noise and Vibration Management Plan (NVMP)
  • Pests Management Plan (PMP)

5. Additionally, Contingency, Emergency, and Climate Change Resilience within the environmental permit management system.

Accident prevention and risk mitigation are essential in the environmental permit management system.

Operators must maintain emergency contingency frameworks that assess the likelihood and consequences of unexpected disruptions.

Additionally, the system must outline proactive preventative actions and emergency response procedures for environmental permit management system.

  • Core equipment breakdowns or sudden utility failures.
  • Enforced or emergency facility shutdowns.
  • Vandalism, security breaches, and deliberate damage.
  • Fires, flash flooding, and severe weather anomalies.

Emergency documentation must include formal accident logging forms, emergency contact directories, and a transparent review schedule. Additionally, operators should actively engage local emergency services and verify flood warning registrations within the environmental permit management system.

Cyber security protocols are essential and an environmental permit management system can support compliance and business continuity.

Modern waste infrastructure and environmental monitoring systems rely heavily on automated computer control systems. Additionally, operators must integrate risk controls aligned with NCSC guidelines to protect software in the environmental permit management system.

Climate Change Adaptation Strategy supports the environmental permit management system to enhance resilience.

In accordance with UK climate projections, operators must evaluate the long-term impact of severe weather shifts on permit compliance. Additionally, these shifts are relevant to the environmental permit management system.

  • Short-to-Medium Term: Operational processes must show resilience against a 2ยฐC global mean temperature rise by 2050.
  • Long-Term Asset Planning: For long-lifecycle facilities, operators must evaluate potential risks up to a 4ยฐC temperature rise by 2100.
  • Methodology: Risk assessments should leverage ISO 14090:2019 standards and the Environment Agencyโ€™s industry sector examples for climate adaptation.

6. Corporate Governance, Training, and Audits

Moreover, staff competence and training infrastructure supports operational effectiveness in the environmental permit management system.

For the environmental permit management system, compliance with the permit requires adequate resource allocation and clearly defined operational roles. Additionally, operators must establish formal procedures.

  • Assign and document individual technical competence responsibilities.
  • Verify external contractor credentials and internal staff qualifications.
  • Maintain central registries of regulatory certifications, safety inductions, and refresher training.

Public Information Provisions outline the environmental permit management system.

Waste and installation permits carry a statutory obligation.

Maintain a clearly visible, weatherproof notice board at the site entrance as part of the environmental permit management system.

The board must display:

  • The registered permit holder’s corporate name.
  • A designated 24/7 emergency contact name and phone number.
  • Explicit confirmation that the facility is regulated by the Environment Agency.
  • The unique environmental permit reference number.
  • Statutory Environment Agency contact numbers: General Enquiries (03708 506506) and the Incident Hotline (0800 807060).

7. Record keeping, auditing, and system reviews support environmental permit management system.

This statutory record retention checklist applies to the environmental permit management system.

Operators must maintain structured archives documenting the active execution of the permit management system. Critical records include:

  • Current and historical environmental permits and legal variations.
  • Comprehensive risk assessments and secondary management plans (e.g., Mops).
  • Detailed calibration records for environmental monitoring and sampling equipment.
  • Logs of all internal compliance checks, audit findings, and remedial actions.
  • Formal complaints ledgers detailing root-cause investigations and resolution outcomes.

Waste Transfer Log Obligations

For every incoming delivery of waste material, operators must capture and preserve the following metrics:

  • Absolute quantity (verified weight or volume).
  • The statutory six-digit List of Waste (LoW) Code.
  • Origin location and complete corporate identity of the waste producer.
  • Date and time of arrival on site.
  • The original generation date (mandatory for odorous or putrescible waste streams).
  • Detailed containment logs for any rejected or quarantined materials.

Mandatory System Review Triggers

A permit management system is a dynamic document. It must be updated immediately upon the occurrence of any of the following events:

  • Technical modifications to onsite machinery, infrastructure, or operational capacities.
  • The submission of an application to vary the existing environmental permit.
  • Post-incident reviews following a site accident, permit breach, or formal complaint.
  • The introduction of new environmental controls to mitigate an emerging risk.

8. Site Closure and Permit Surrender

Environmental permits cannot be abandoned unilaterally when operations cease. Legal obligations remain active until the Environment Agency formally approves a Permit Surrender Application.

For landfills and Category A mining waste facilities, a transitional period of site closure applies. During this phase, operators must maintain active emissions monitoring regimes and submit final site closure updates via the Site Condition Report, proving conclusively that the land and groundwater have been returned to a satisfactory state.

Technical Support and Consultancy

Developing, implementing, and defending a regulatory management system requires specialist technical oversight. For bespoke assistance with permit applications, Fire Prevention Plans, or standalone environmental management documents, contact our regulatory advisory team for professional consultation.